OAuth2 Shared Token Policy (Chain Policy)
This is a Chain Custom Policy that can be used to chain multiple processors and Traffic Event Listeners. Refer to Chaining Processors for more information about chain policies.
Description
-
Share OAuth2 token to access backend resources for multiple OAuth2.0 protected service endpoints.
-
OAuth shared token Policy uses
spkey(API definition key or service package key) of API service where the access token was generated. -
Access token created for API service 'X' allows authenticating API Service 'Y' with the same token.
Prerequisites
Before configuring values on the Call Transformation page for this policy, ensure you have set the following values for your endpoint on the Key & Method Detection:
- Endpoint Type: REST
- Supported Http Methods: GET and POST
- Method Location: PATH
- Request Authentication Type: OAuth 2.0
- OAuth Grant Types: Authorization Code, Implicit, Password, Client Credentials
Design and Implementation
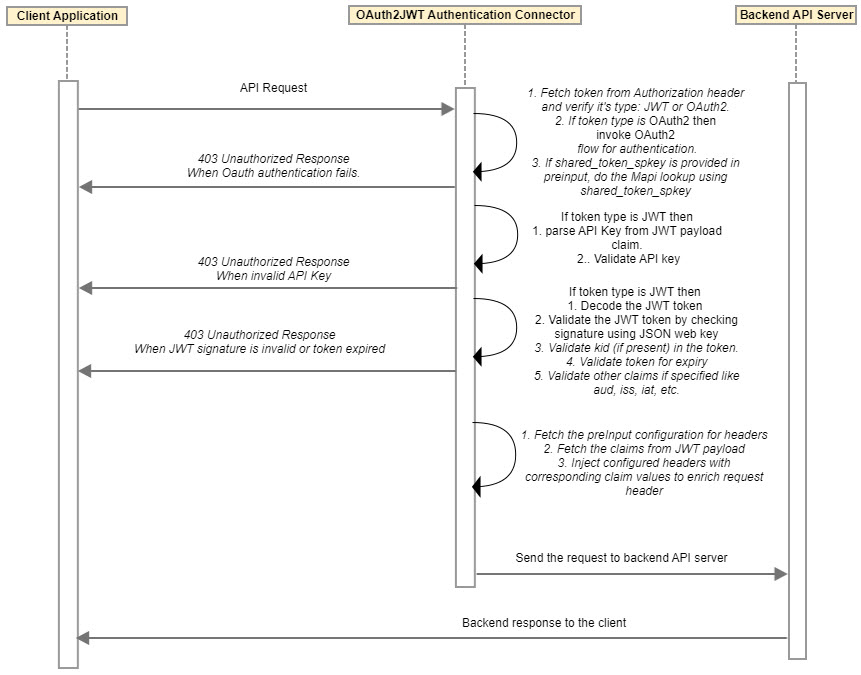
Sequence Diagram
Implementation
-
If policy is configured for pre-processing, then pre-input configurations are retrieved and shared token
spkeyis fetched from pre-input configuration. -
In case shared token
spkeyis not defined in pre-input configuration, then default oauth context is loaded and mapi look-up is done using specifiedspkeyin service configuration. -
If shared token
spkeyis defined in pre-input configuration, service configuration is loaded using this shared tokenspkeyand oauth context is created using this service configuration. -
Also in case shared token
spkeyis specified in pre-input configuration, then originalspkeyis stored and replaced by sharedspkey. Then mapi look-up is done using this sharedspkey. After mapi look-up, originalspkeyis restored in the service configuration.
